GitHub Copilot 代码审查配置教程
Copilot 可以审查 GitHub 上的每一个 Pull Request:手动请求一次审查、一键应用它给出的修改建议,再用 rulesets 把它变成强制流程。16 个图解步骤,全部来自 GitHub 官方录屏。
快速结论:四步配好 Copilot 代码审查
- 打开 Pull Request,在 Reviewers → Copilot 旁点 Request。Copilot 的总览评论和行内建议通常 30 秒内就会到达。
- 用 Commit suggestion 按钮一键采纳修改,不用打开 IDE。Copilot Autofix 的修复提交后,code scanning 会自动重跑并关闭告警。
- 想强制执行:在 ruleset 里勾选 Require a pull request before merging,再勾上 Automatically request Copilot code review,每个新 PR 都会自动获得 Copilot 审查。
- 把团队规范写进 .github/copilot-instructions.md;再用仓库根目录的 AGENTS.md 和按路径生效的 .instructions.md 文件细化 Copilot 的审查重点。
一步步配好 GitHub Copilot 代码审查
读懂 Pull Request 上的 Copilot 审查
- 1
打开 Pull Request,在 Reviewers 里找到 Copilot
Pull Request 一创建,Copilot 就会出现在 Reviewers 区——要么是你手动添加的,要么是 ruleset 自动请求的。时间线里的 "review requested due to automatic review settings" 就是自动化已生效的标志。
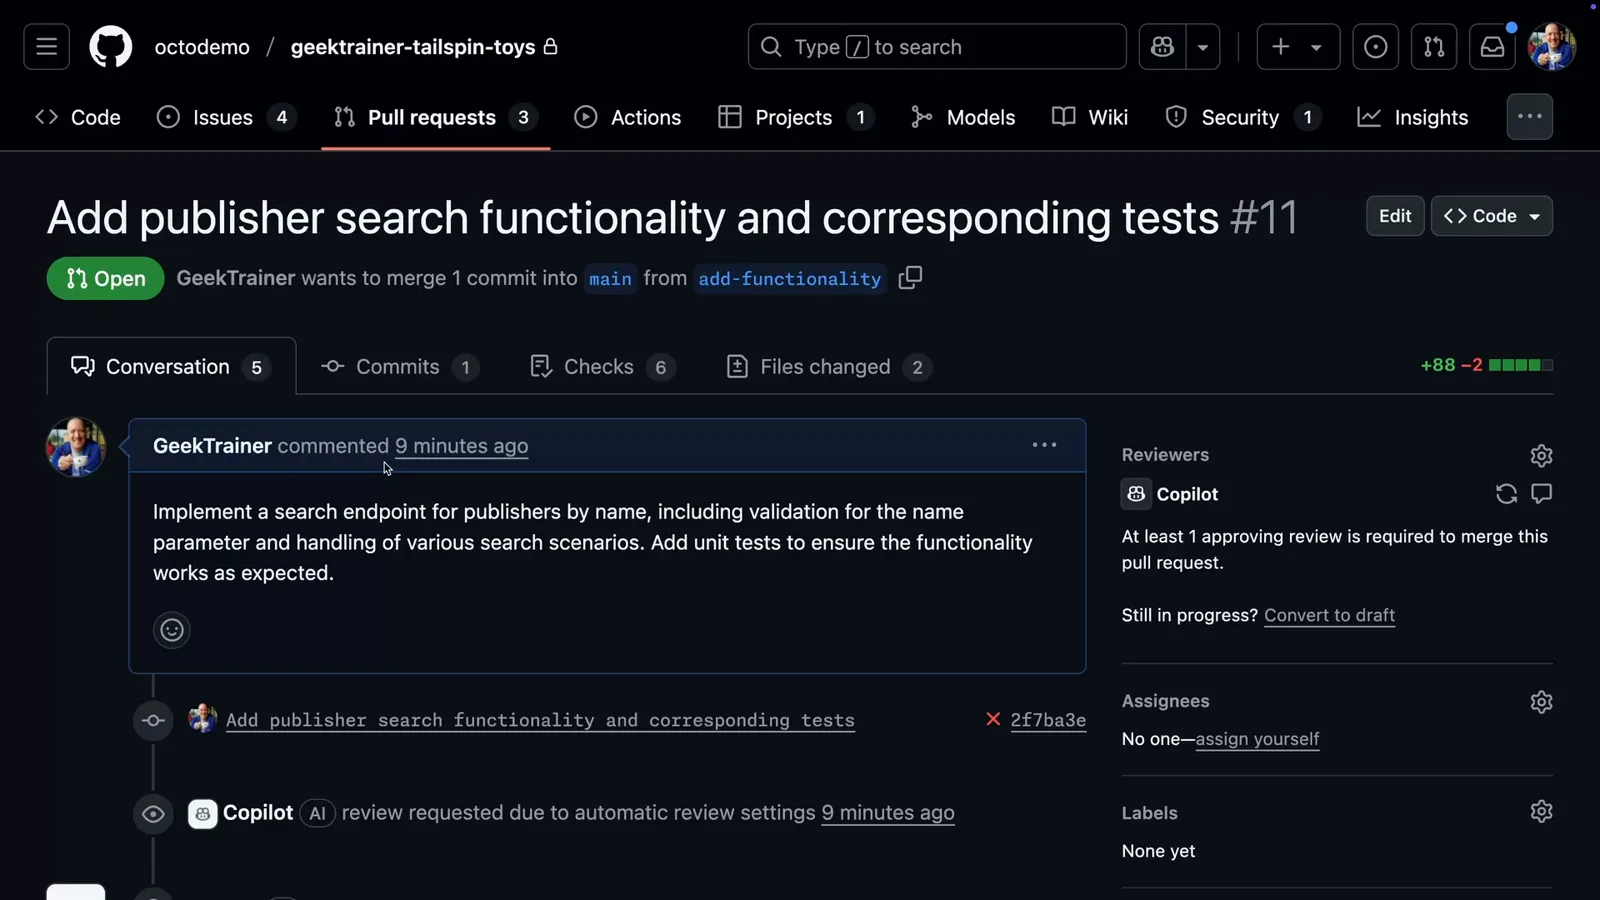
PR 一开,Copilot 就进了审查队列。去视频 0:10 处观看 - 2
先读 Copilot 的 Pull Request Overview
Copilot 的第一条评论是总览:这个 PR 做了什么、审查了哪些文件、生成了几条意见。把它当成整场审查的目录来用。
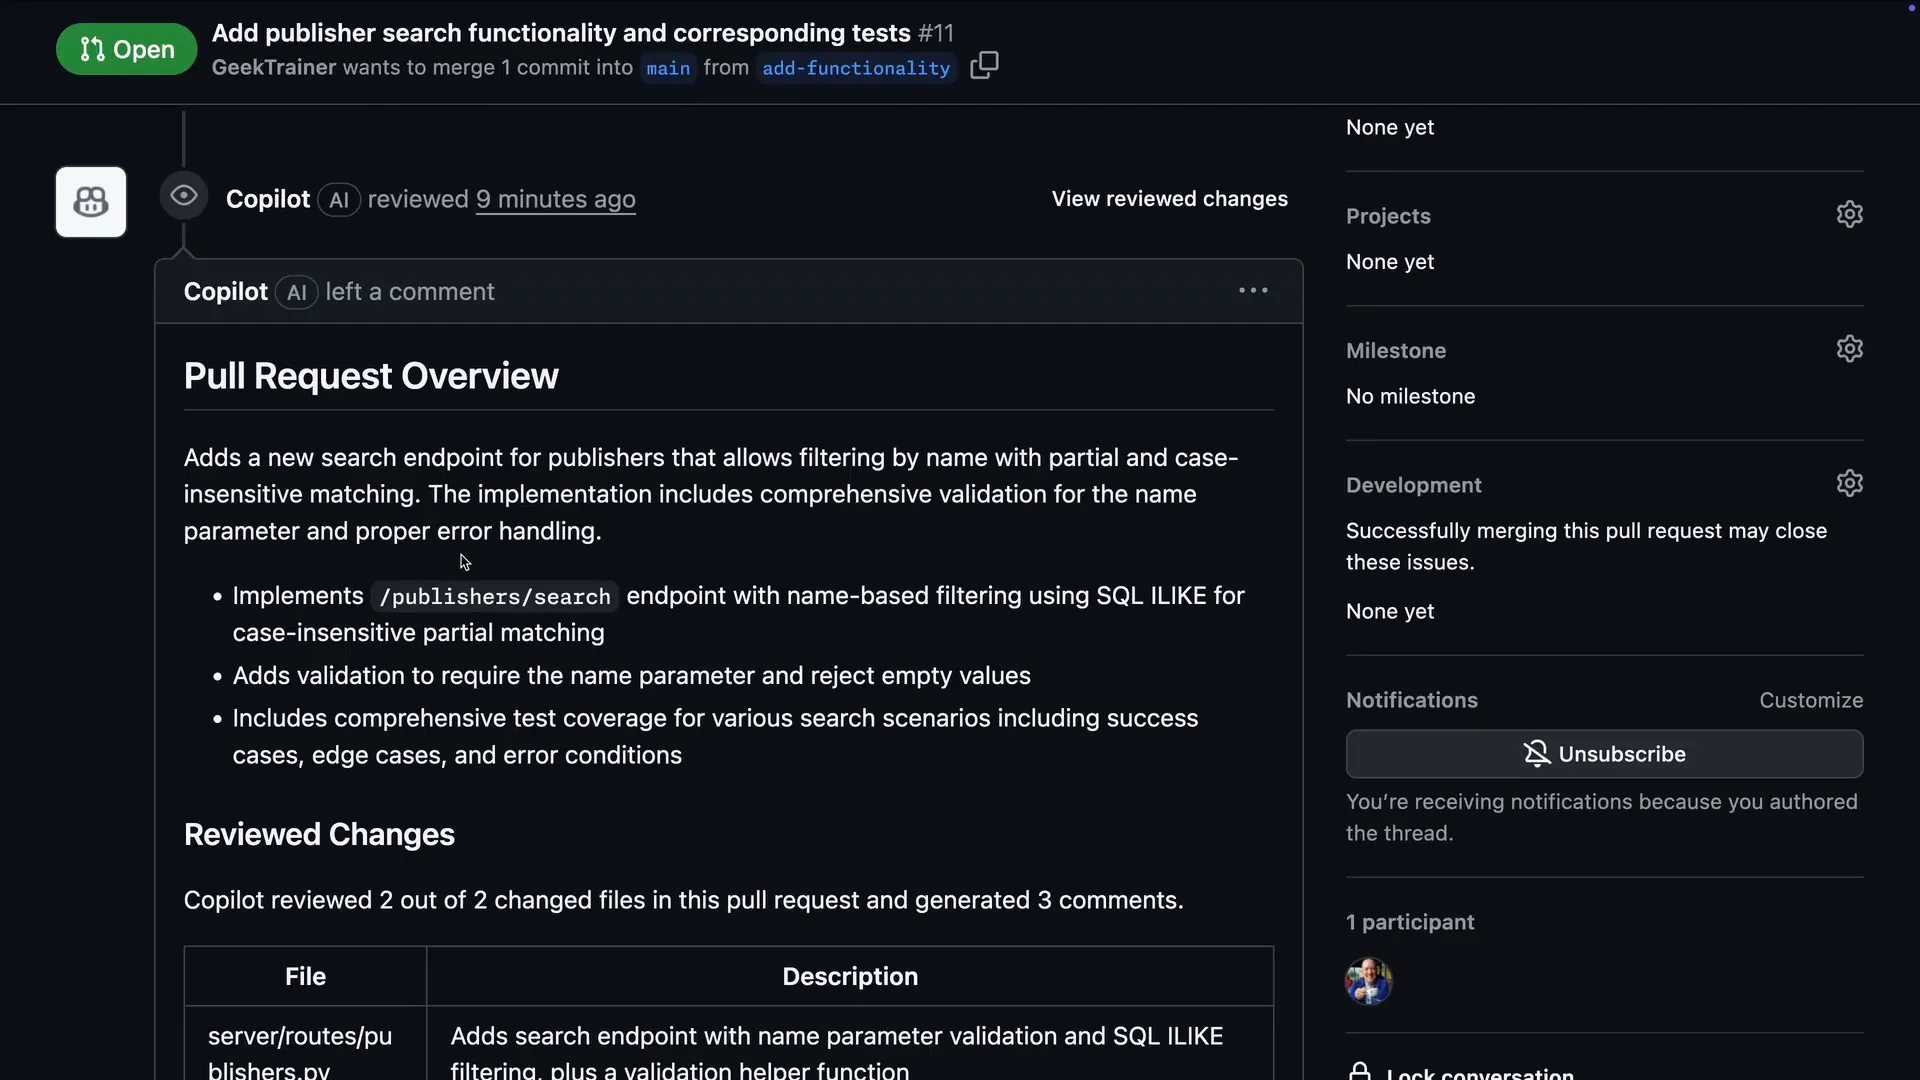
在读任何行内意见之前,总览评论先告诉你 Copilot 看了什么。去视频 0:20 处观看 - 3
逐条阅读带修改建议的行内评论
行内评论精确落在出问题的代码行上。这条把 exec() 加字符串拼接标记为代码注入风险,并在下面附上了可直接采纳的建议代码块。
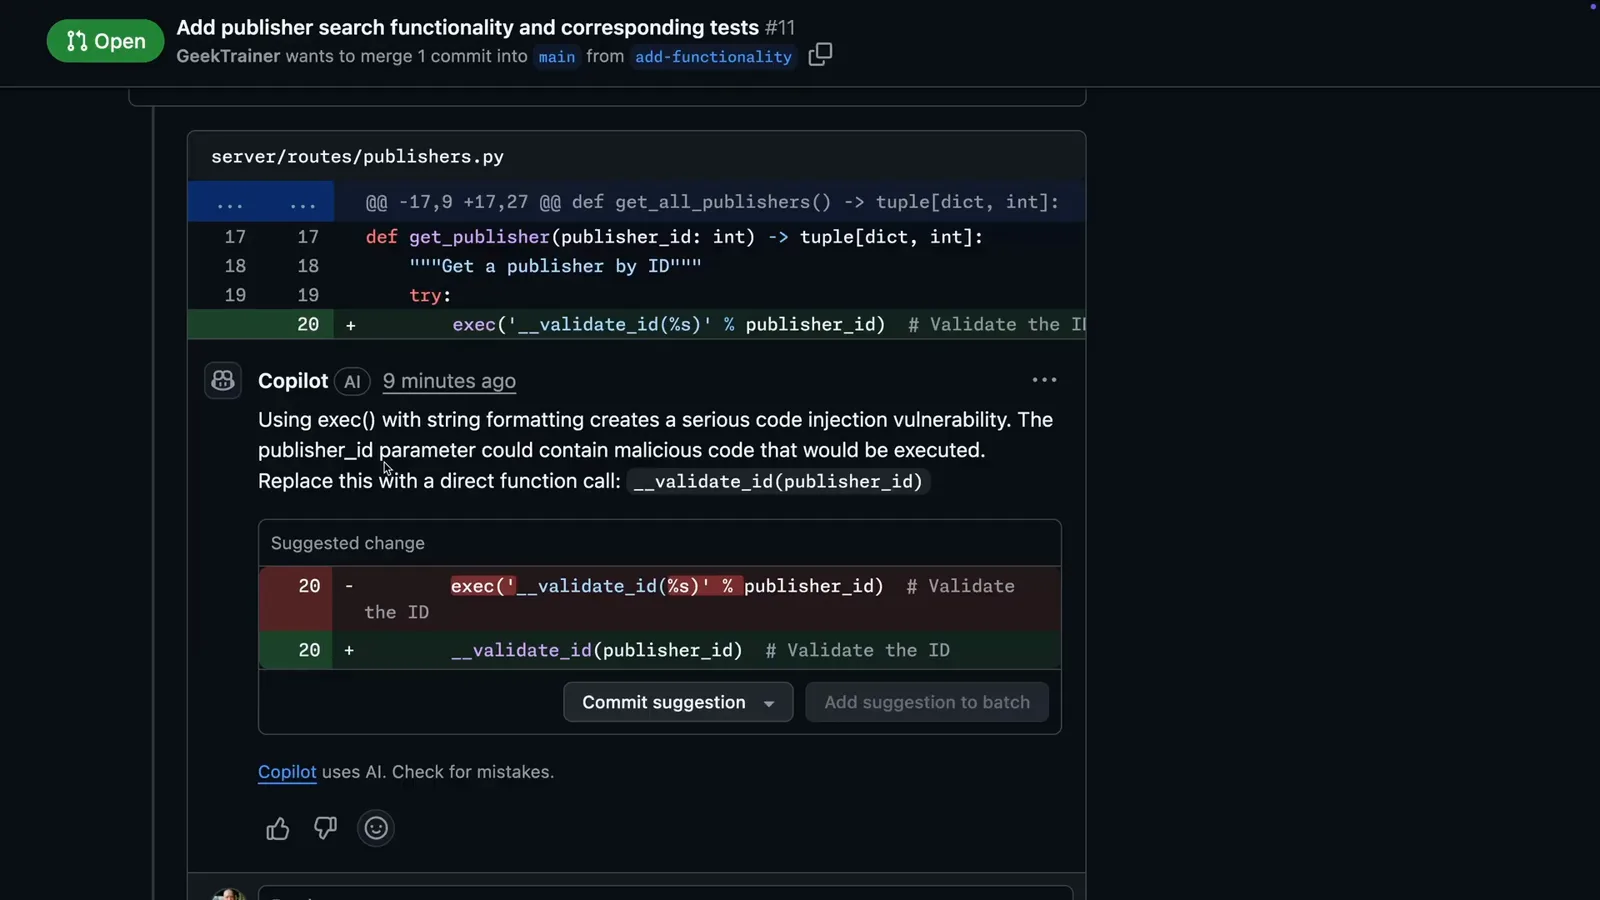
严重的先说:注入警告自带一键采纳的建议修改。去视频 0:32 处观看 - 4
查看风格与类型注解类的意见
Copilot 也会执行你仓库自己的约定——这里它引用了编码规范,并给出应该补充的准确注解。评论下方的 👍/👎 按钮可以反馈意见质量,帮助改进之后的审查。
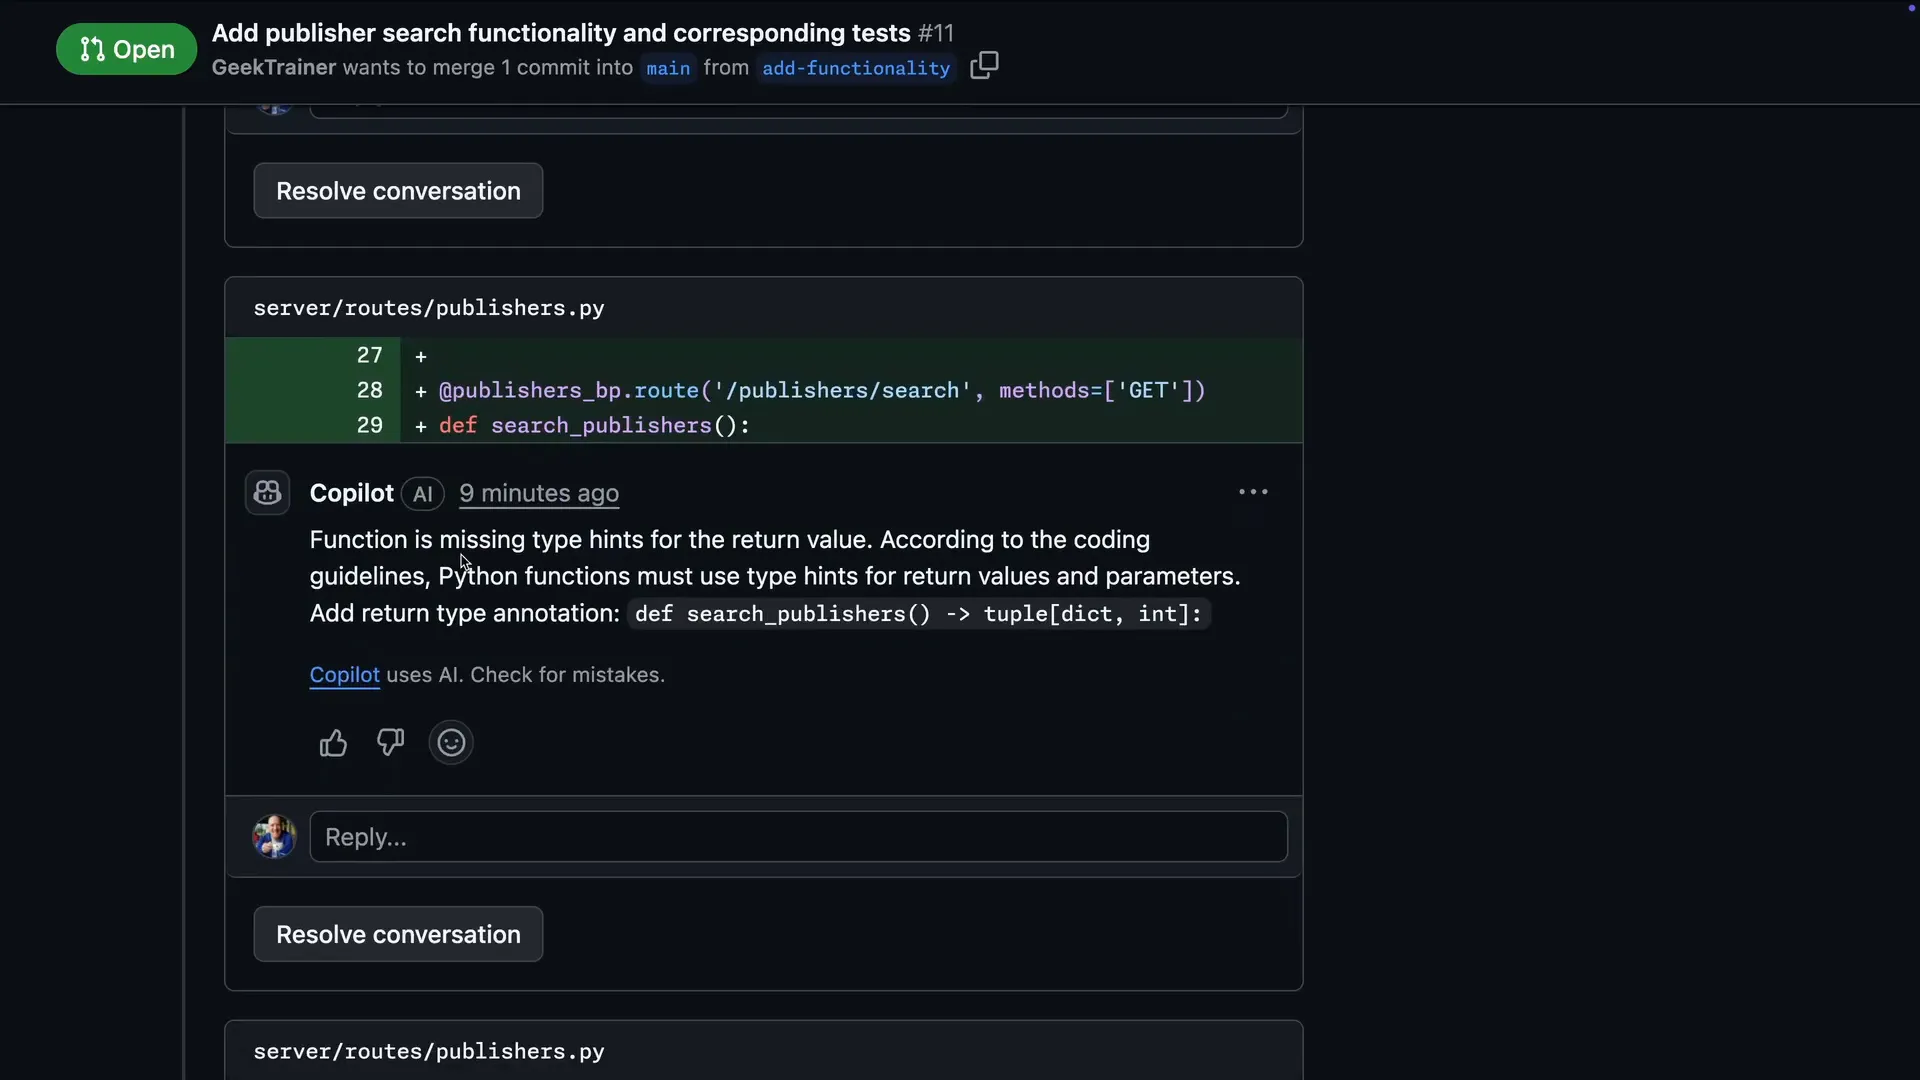
规范类意见会把你自己写的准则原样引用回来。去视频 0:52 处观看
修复 Copilot 和 code scanning 标出的问题
- 5
把 Copilot 的发现与 code scanning 对照
github-advanced-security 机器人把同一处 exec() 上报为 CodeQL 代码注入告警。告警下方,Copilot Autofix 附上了漏洞解释和修复方案。
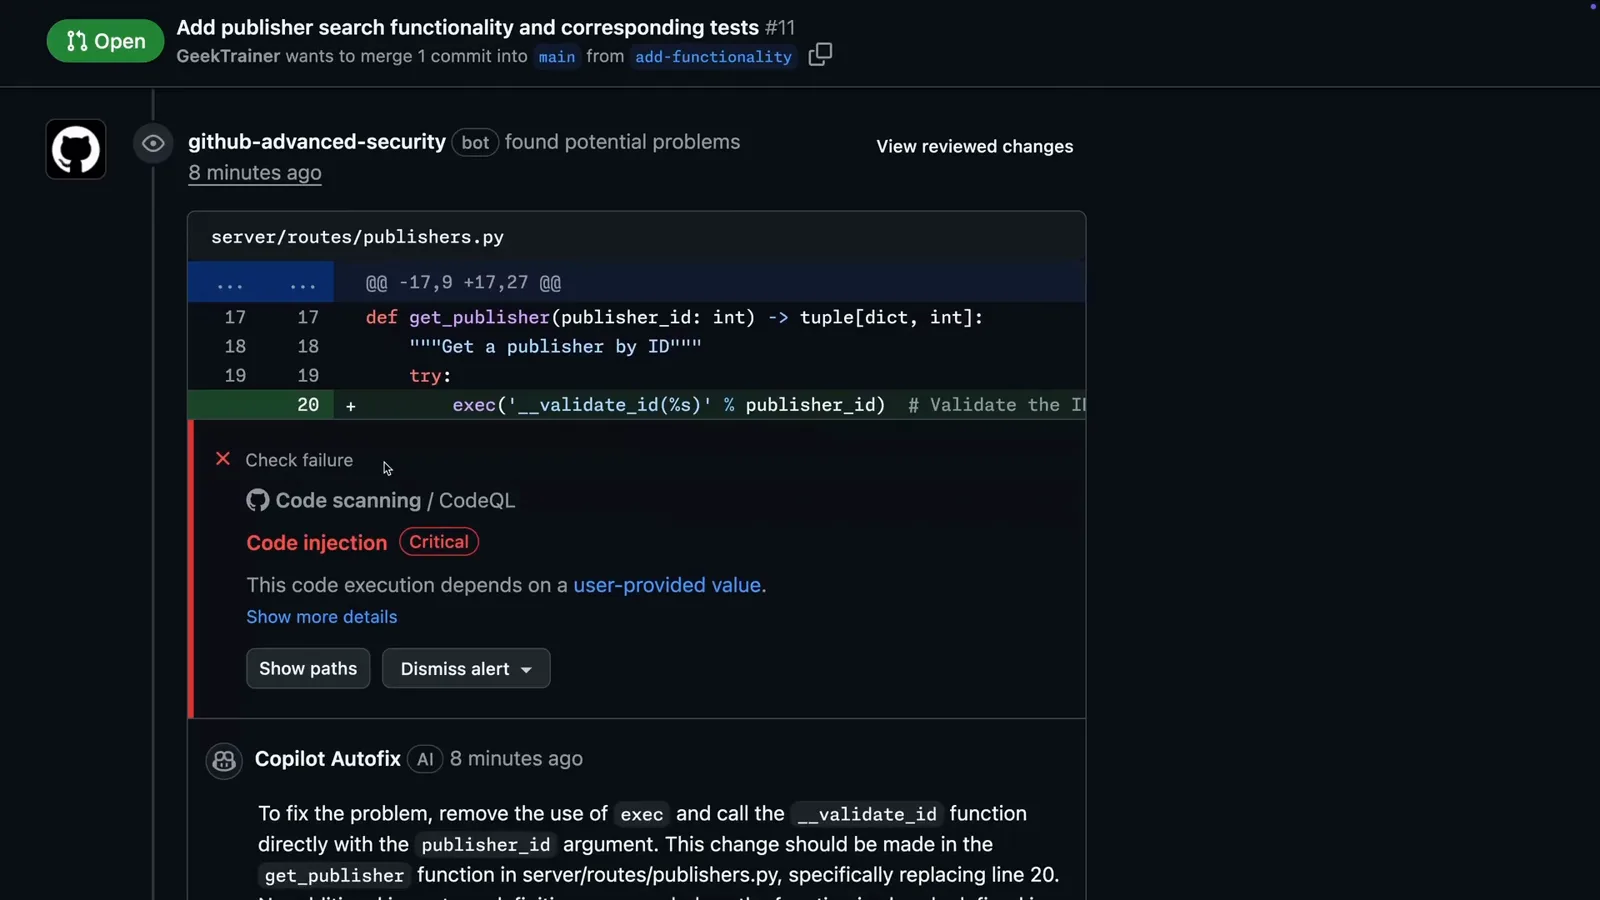
两位审查者盯同一行:CodeQL 报警,Copilot Autofix 开药。去视频 1:08 处观看 - 6
一键采纳建议修改
每个建议代码块都带 Commit suggestion 按钮——修复会作为新提交直接落到 PR 分支上,全程不用打开 IDE。也可以把多条建议合并成一次提交。
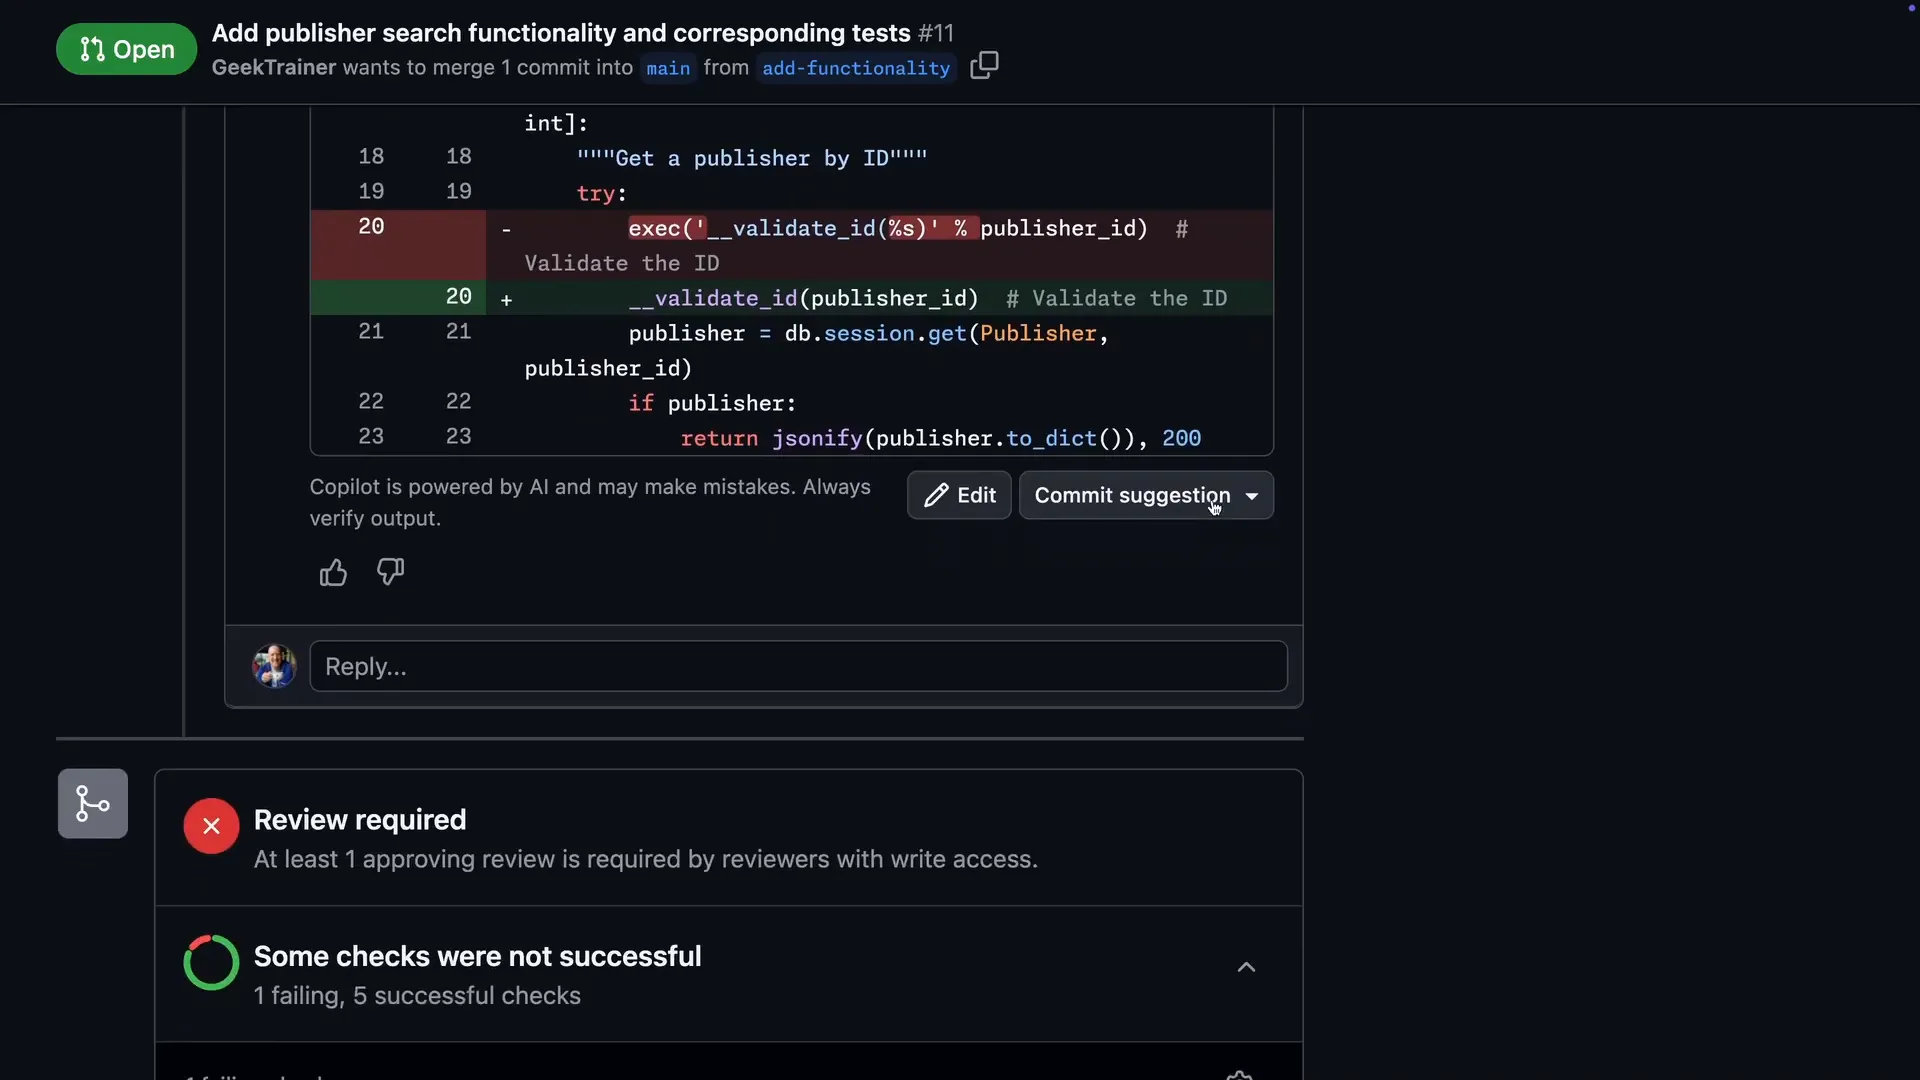
Commit suggestion 会把修复直接写进 PR 分支。去视频 1:23 处观看 - 7
看 code scanning 自动重跑
采纳 Autofix 建议后会出现 "Alert fix successfully applied" 横幅,PR 多出第二个提交,CodeQL 随即重新扫描分支——修复有效的话,告警会自动关闭。
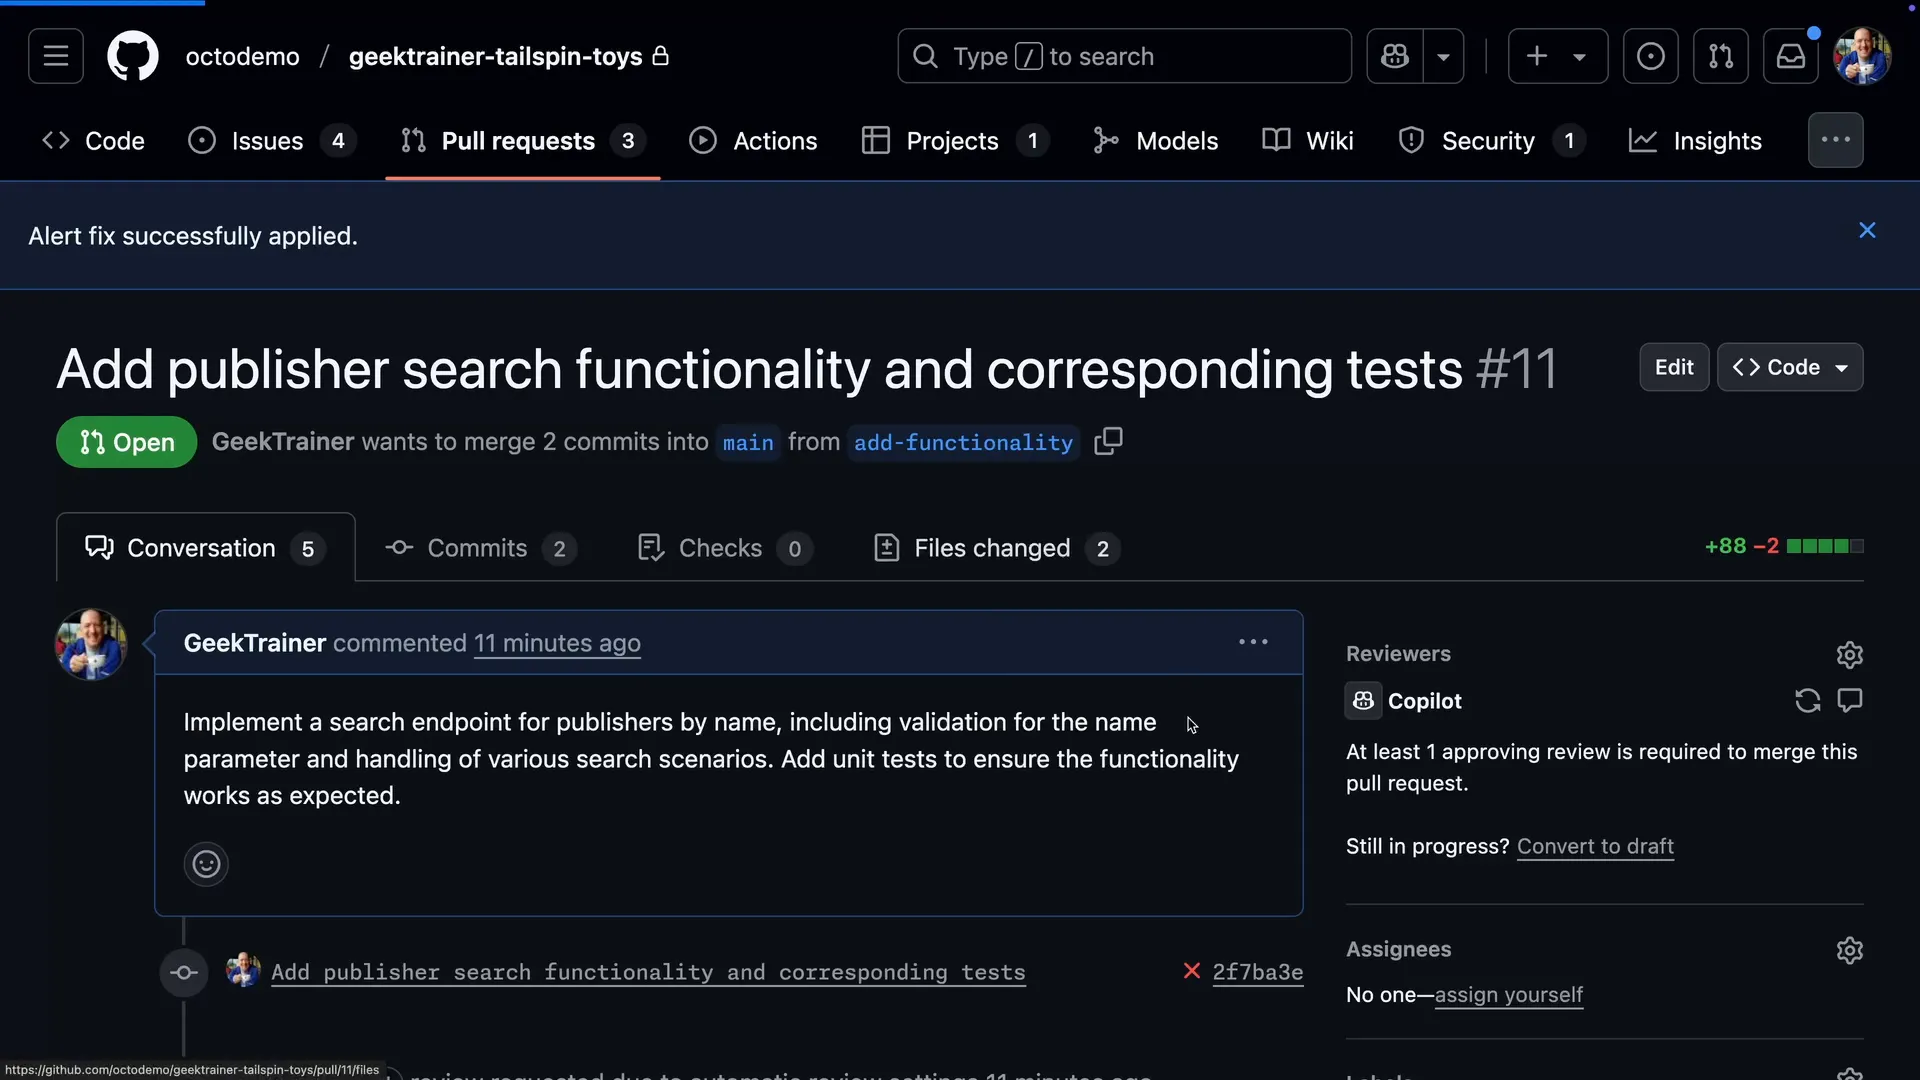
修完即复检:修复提交之后 CodeQL 会验证整个分支。去视频 1:46 处观看 - 8
在 Files 标签页里清掉剩余意见
Files changed 标签页会把 Copilot 的评论并排显示在 diff 旁。在这里打开 Apply suggestion,按需改一下提交信息,直接提交——不用回到编辑器。
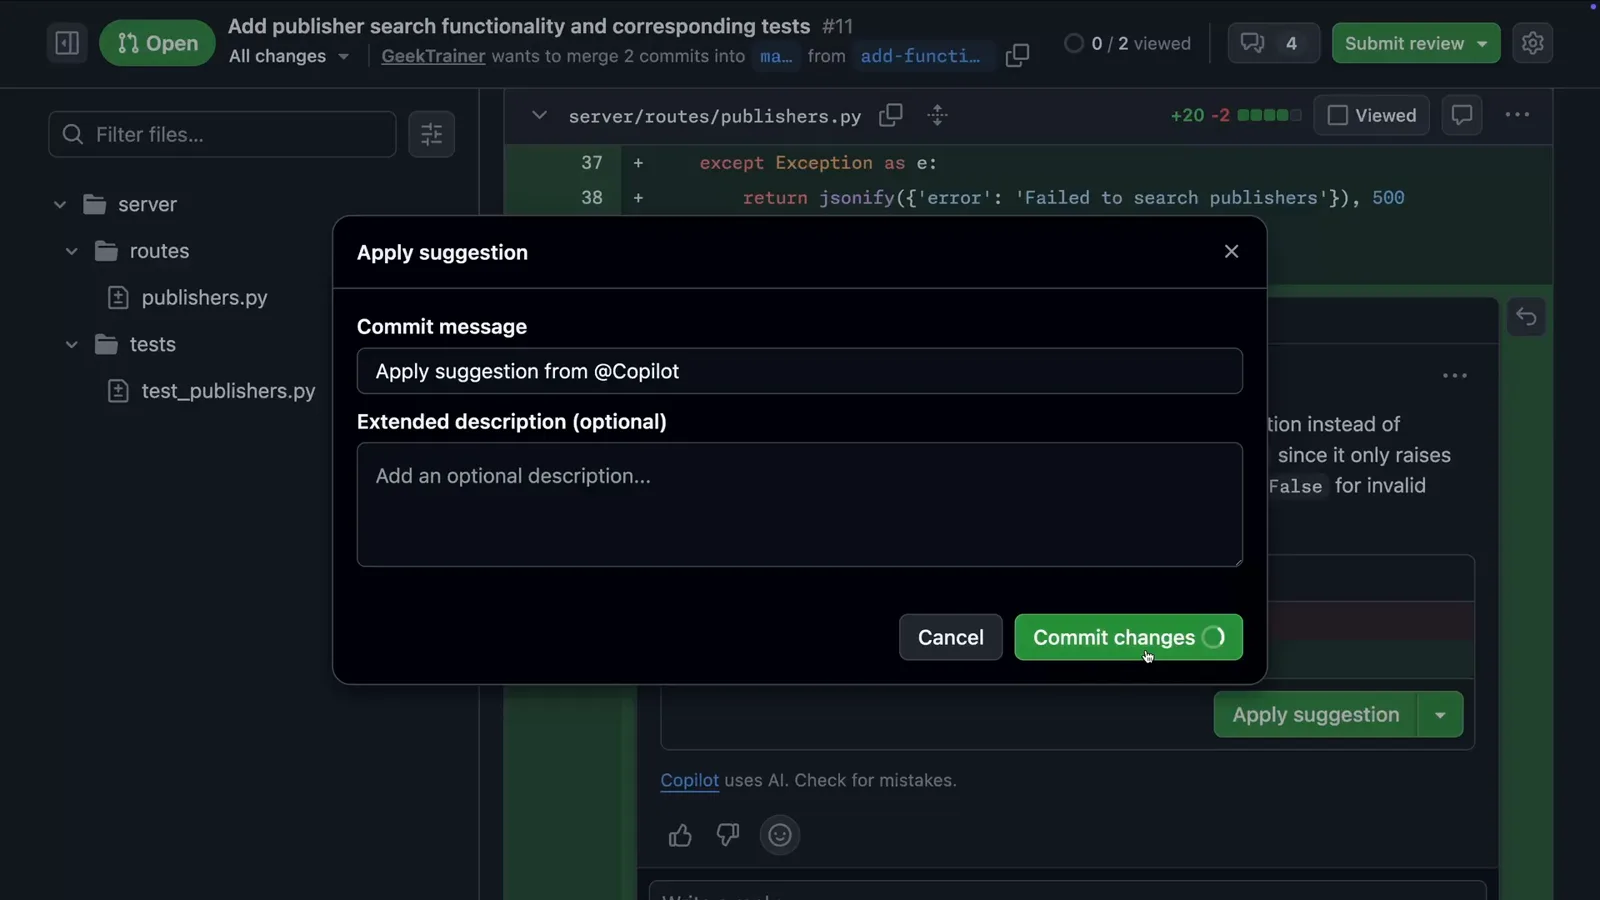
审查评论连同建议一起挂在 Files 标签页的 diff 旁。去视频 2:02 处观看
用 rulesets 和指令文件把审查变成强制项
- 9
建一个自动请求 Copilot 审查的 ruleset
在 Settings → Rulesets → New ruleset 里,目标分支选默认分支,展开 Require a pull request before merging,把 Required approvals 设为 1,再勾选 Automatically request Copilot code review。此后每个新 PR 都会自动获得 Copilot 审查,没人需要记得手动点 Request。
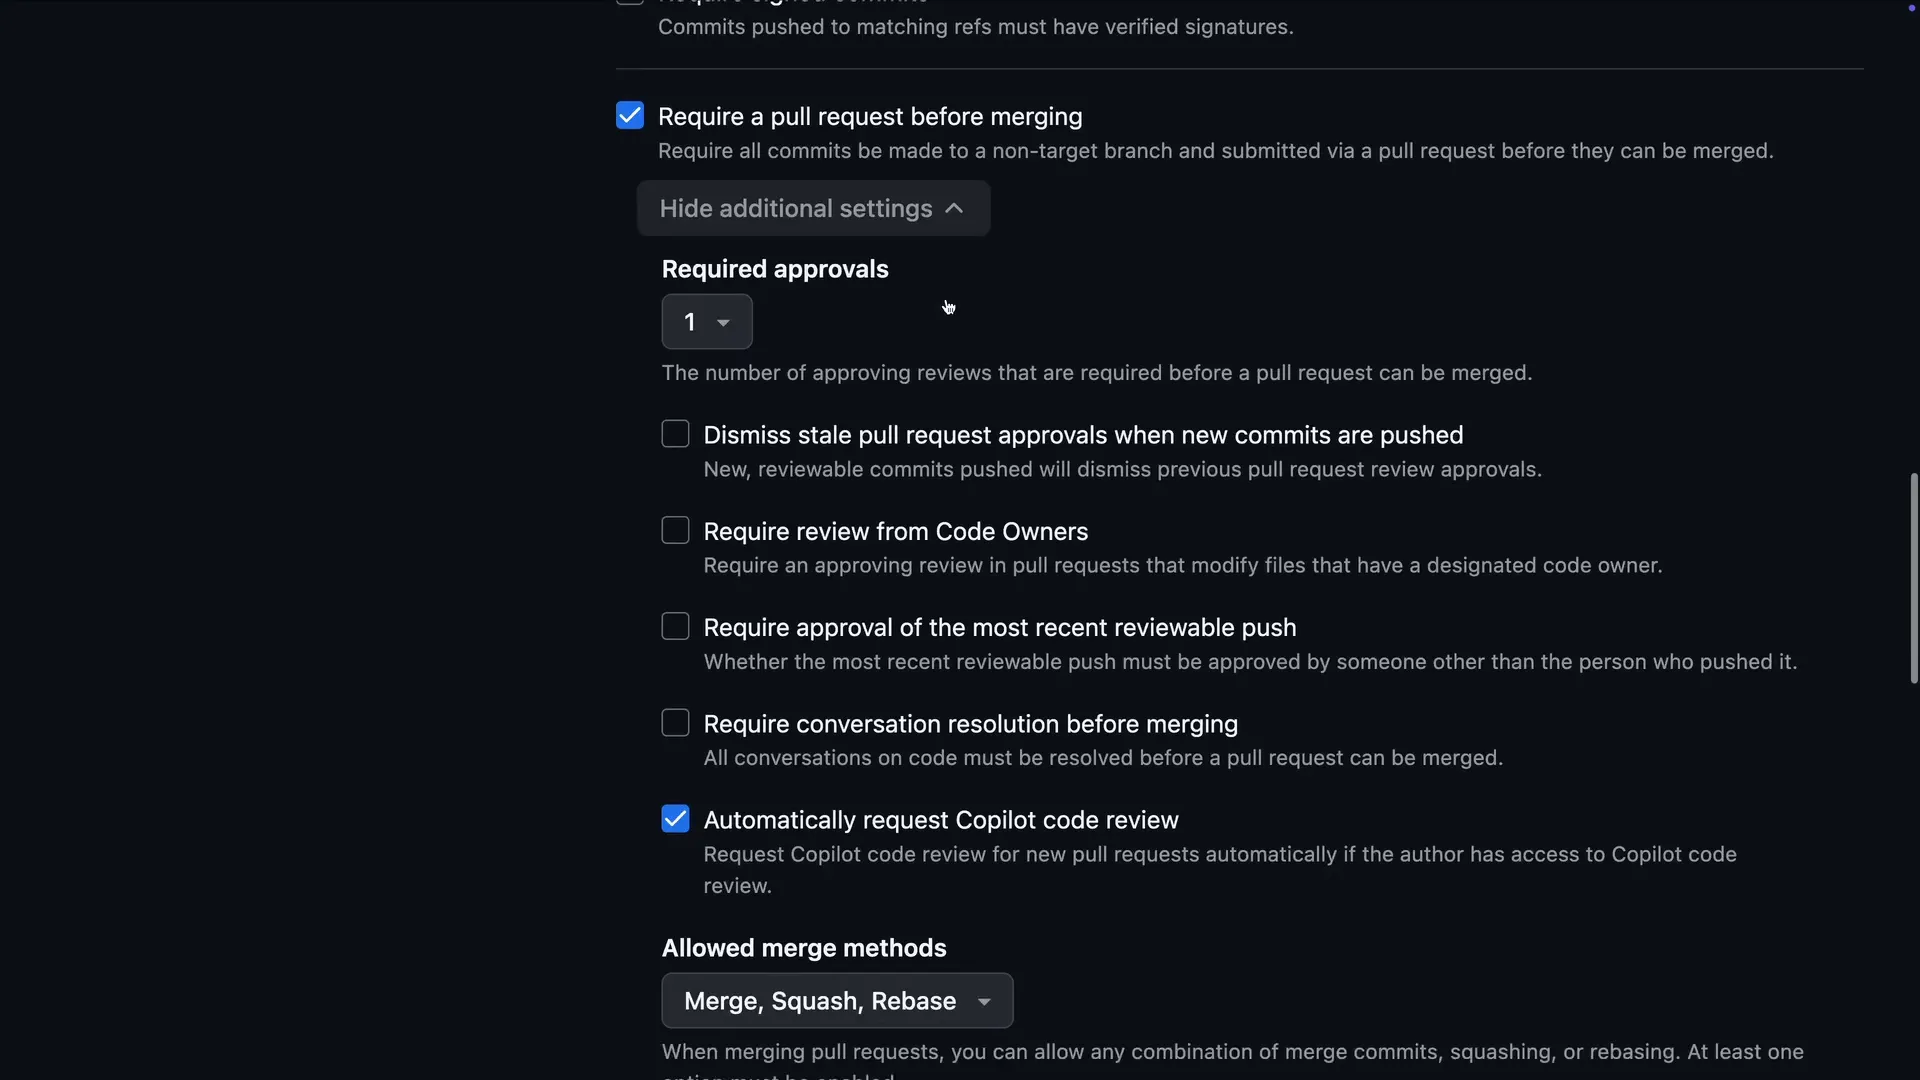
勾上这个框,目标分支上的每个新 PR 都会自动获得 Copilot 审查。去视频 2:26 处观看 - 10
把守门的状态检查设为必需
在同一个 ruleset 里启用 Require status checks to pass,把 GitHub Actions 工作流里的 backend-tests 和 frontend-tests 加进来。从此合并必须等绿灯。
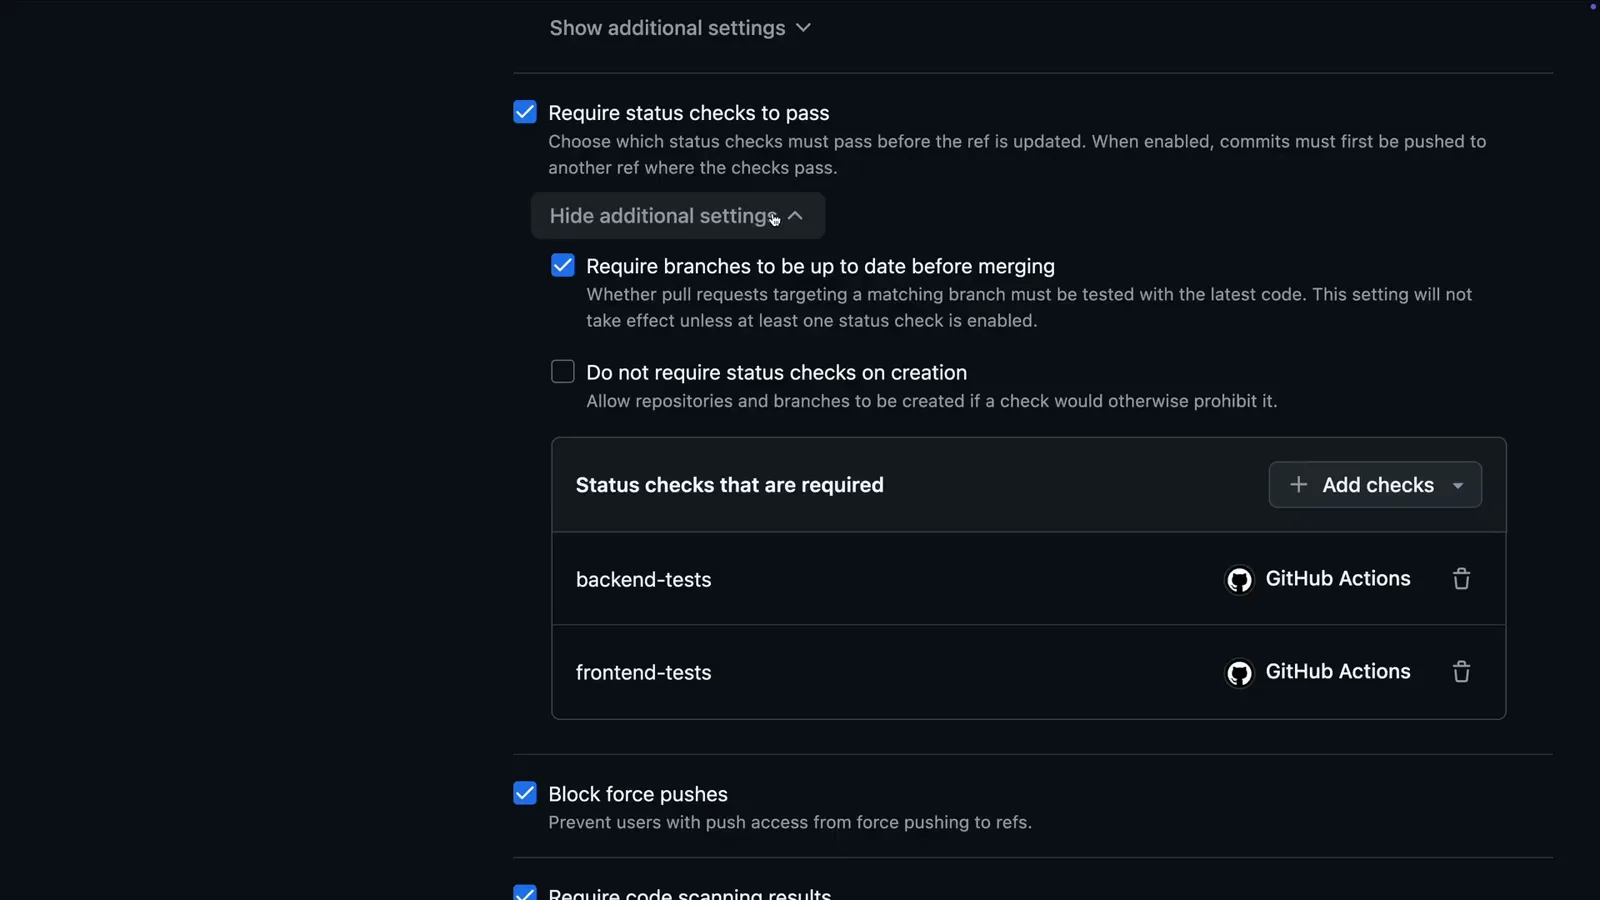
仓库 Actions 里的两个工作流任务,现在把守着每一次合并。去视频 2:32 处观看 - 11
有未处理的安全告警就禁止合并
还在这个 ruleset 里,勾选 Require code scanning results,添加 CodeQL 并设定阈值——Security alerts: High or higher、Alerts: Errors。高危发现会把合并冻住,直到问题修复。
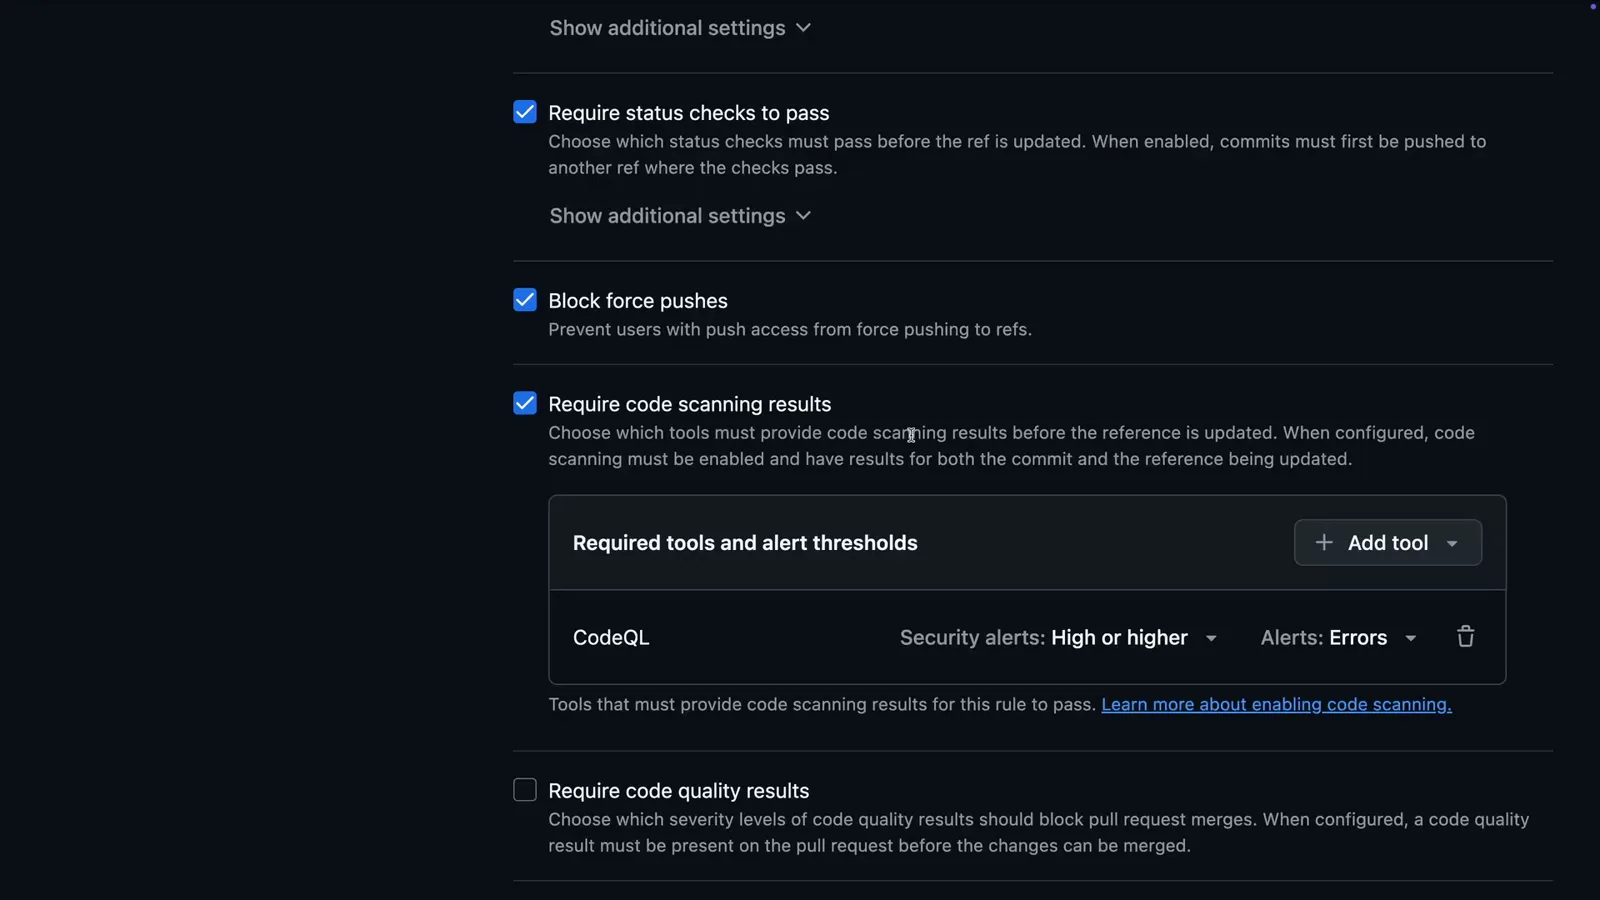
CodeQL 的阈值决定哪些告警会冻住一个 PR。去视频 2:42 处观看 - 12
把团队规范白纸黑字写给 Copilot
在仓库里添加 .github/copilot-instructions.md,写清技术栈和规则——Copilot Review 每次审查都会读这个文件,并在评论里引用你写的规范。
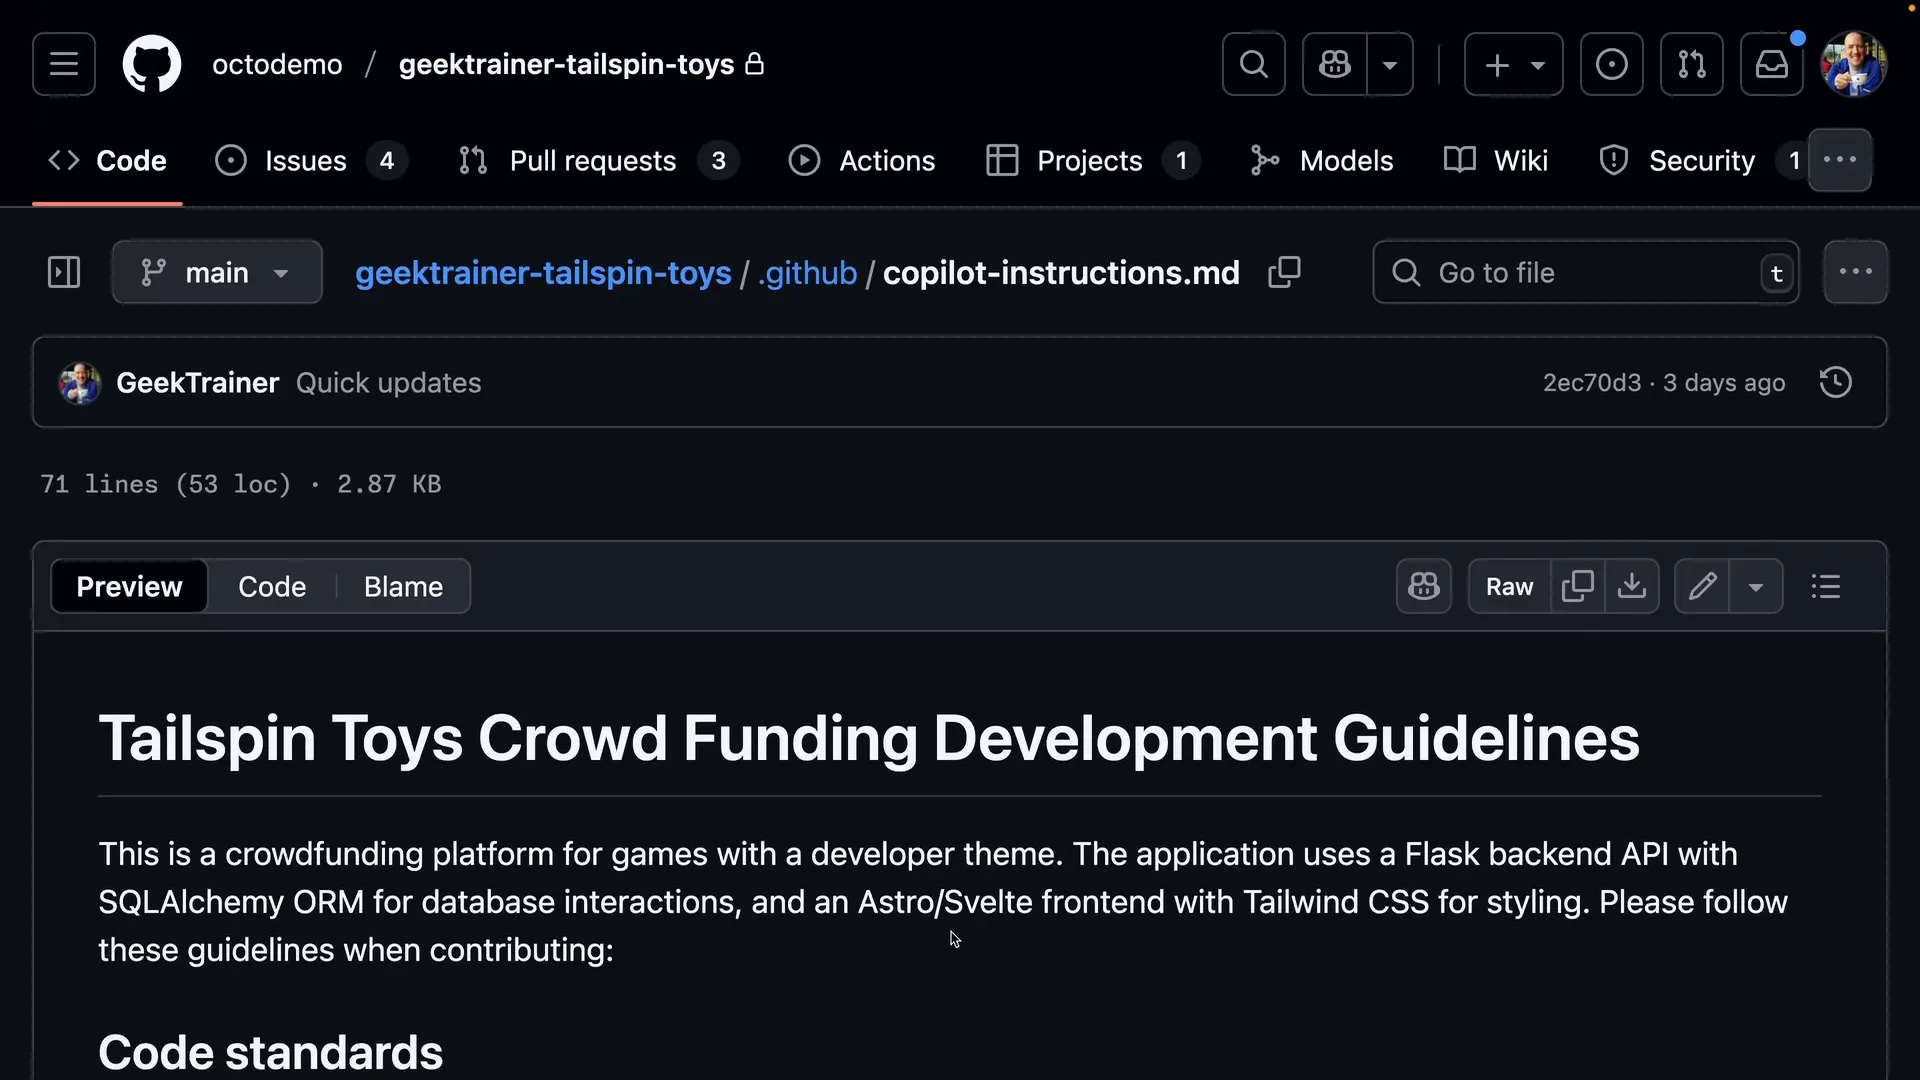
文件放在 .github 目录下,每次 Copilot 审查都会继承它。去视频 2:53 处观看
审查 Copilot 自己提交的 Pull Request
- 13
把 Copilot 的 PR 当成同事的来审
Copilot 自己也会提交 Pull Request——它的代码同样需要人工把关。打开它的 PR,读一遍它写的描述,确认合并前必须有人类审查者批准。
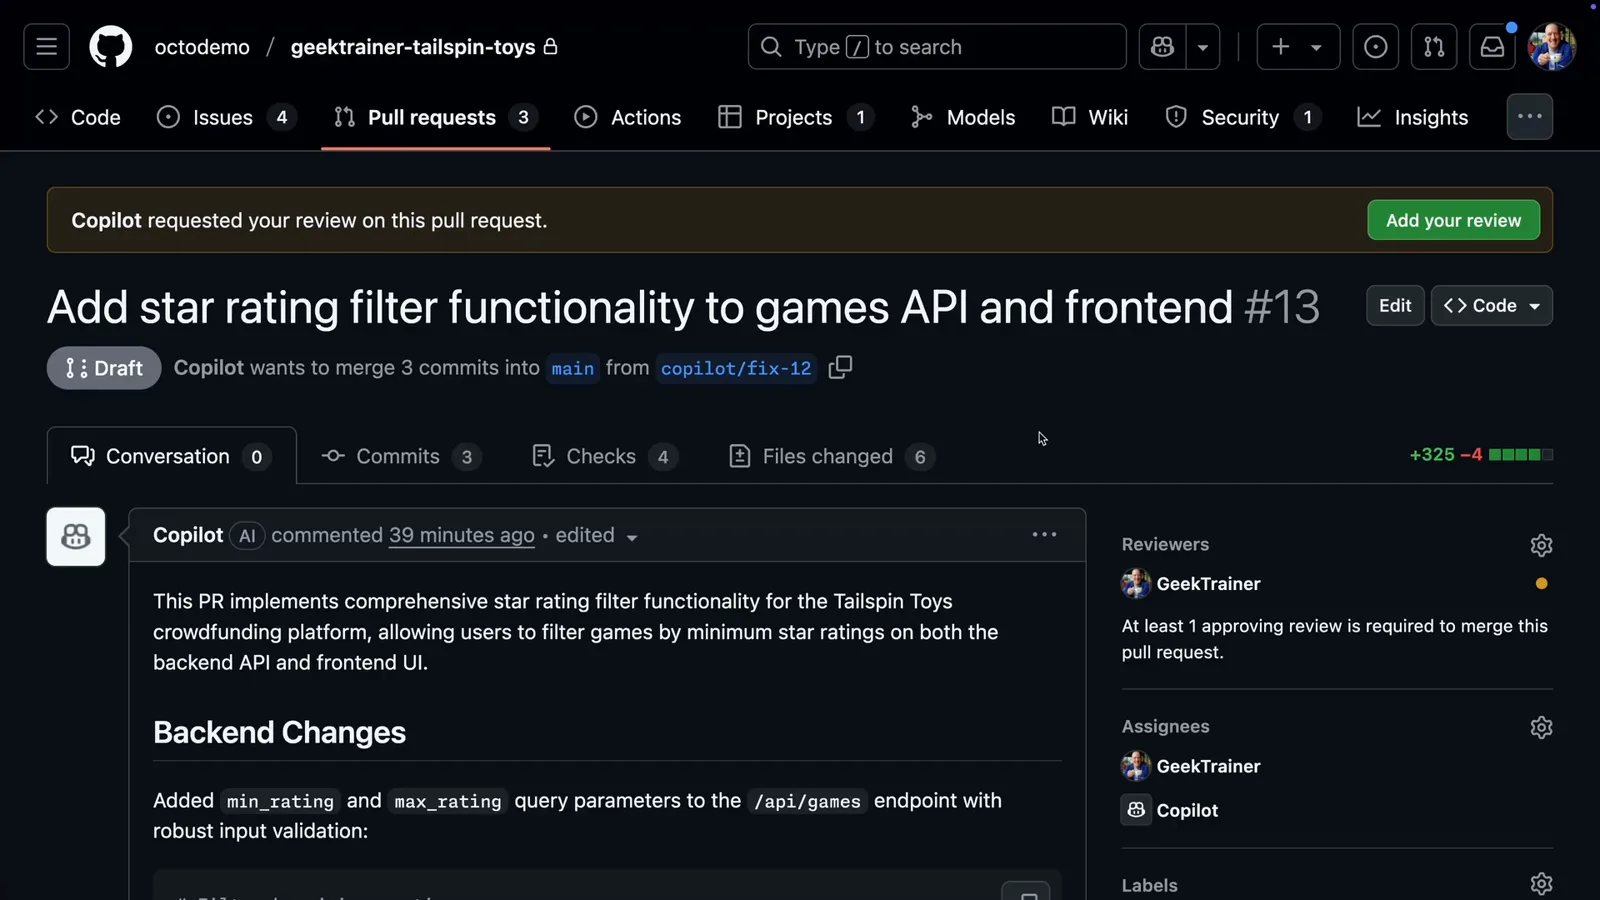
Copilot 从 copilot/fix-12 分支发起了这个 PR,并主动请求人类审查。去视频 3:12 处观看 - 14
批准之前先在 codespace 里跑一遍
在 Copilot 的分支上打开 codespace,把应用跑起来。Copilot 写的星级筛选确实能用——所以别只读 diff,动手点一点。
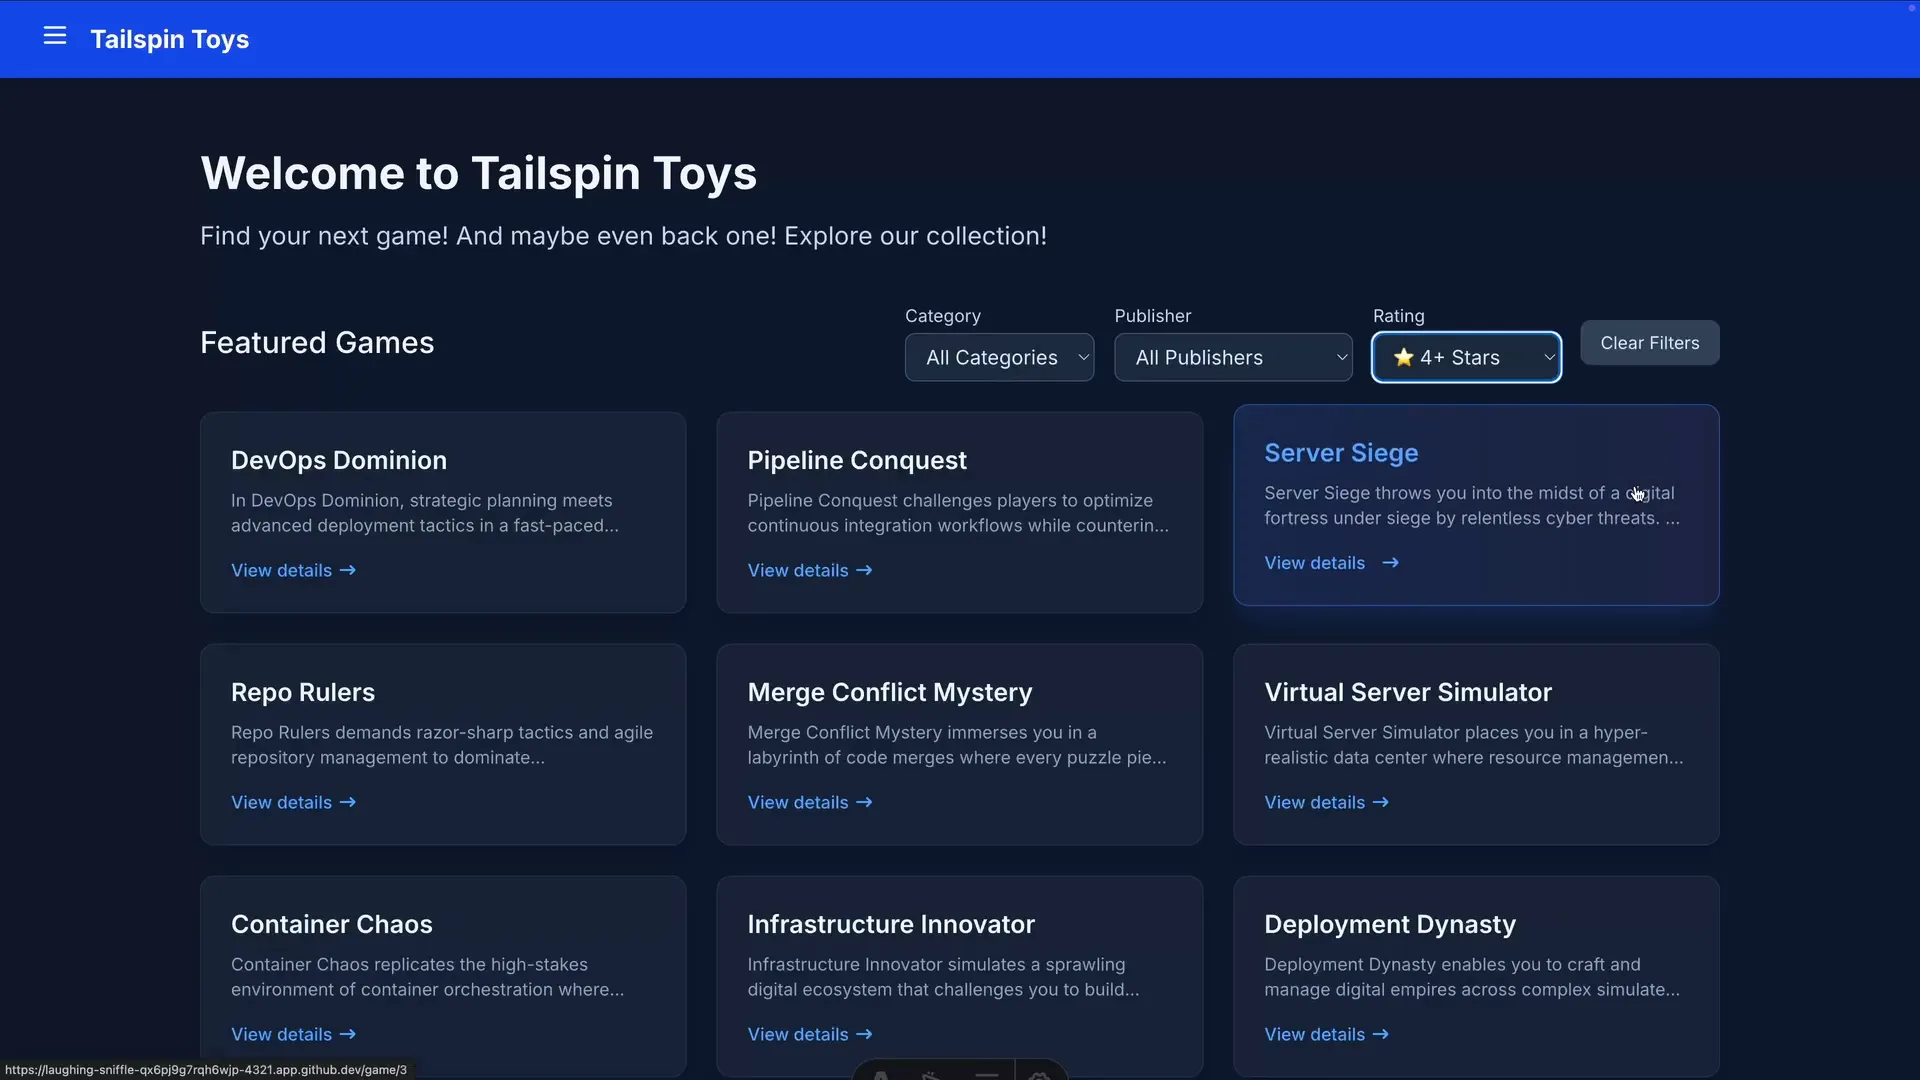
codespace 的 URL 直接跑着 Copilot 的分支——筛选设为 4+ 星。去视频 3:42 处观看 - 15
用 @copilot 评论要求改代码
发现不足?在 PR 里评论并 @copilot,写清具体要求。Copilot 会把后续提交推到同一个 PR 上——绝不抱怨需求蔓延。
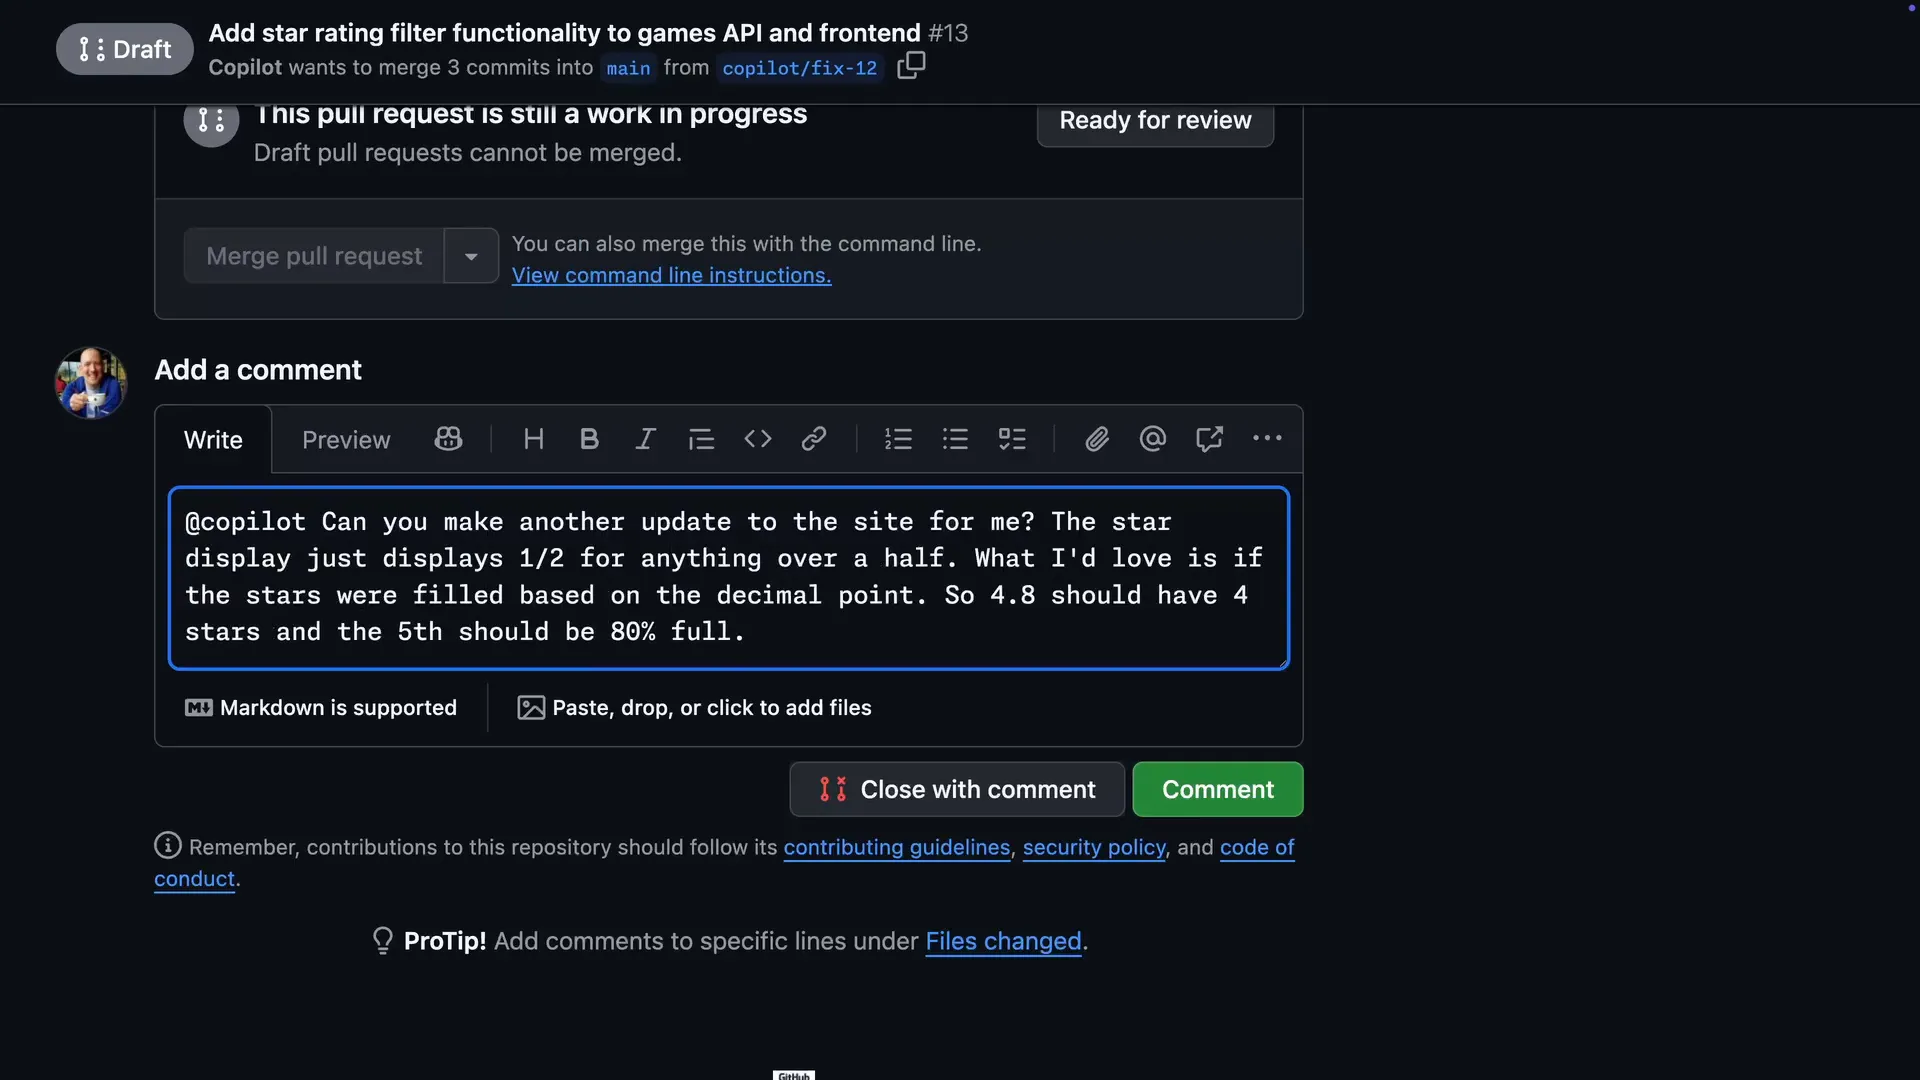
一条 @copilot 评论就够把 agent 派回去干活。去视频 3:57 处观看 - 16
批准 Copilot PR 上的 workflow 运行
出于安全考虑,Copilot 作者的 PR 上 Actions 会保持排队,直到有人类点下批准。按 Approve workflows to run,然后等 backend-tests、frontend-tests 和 CodeQL 全部变绿再合并。
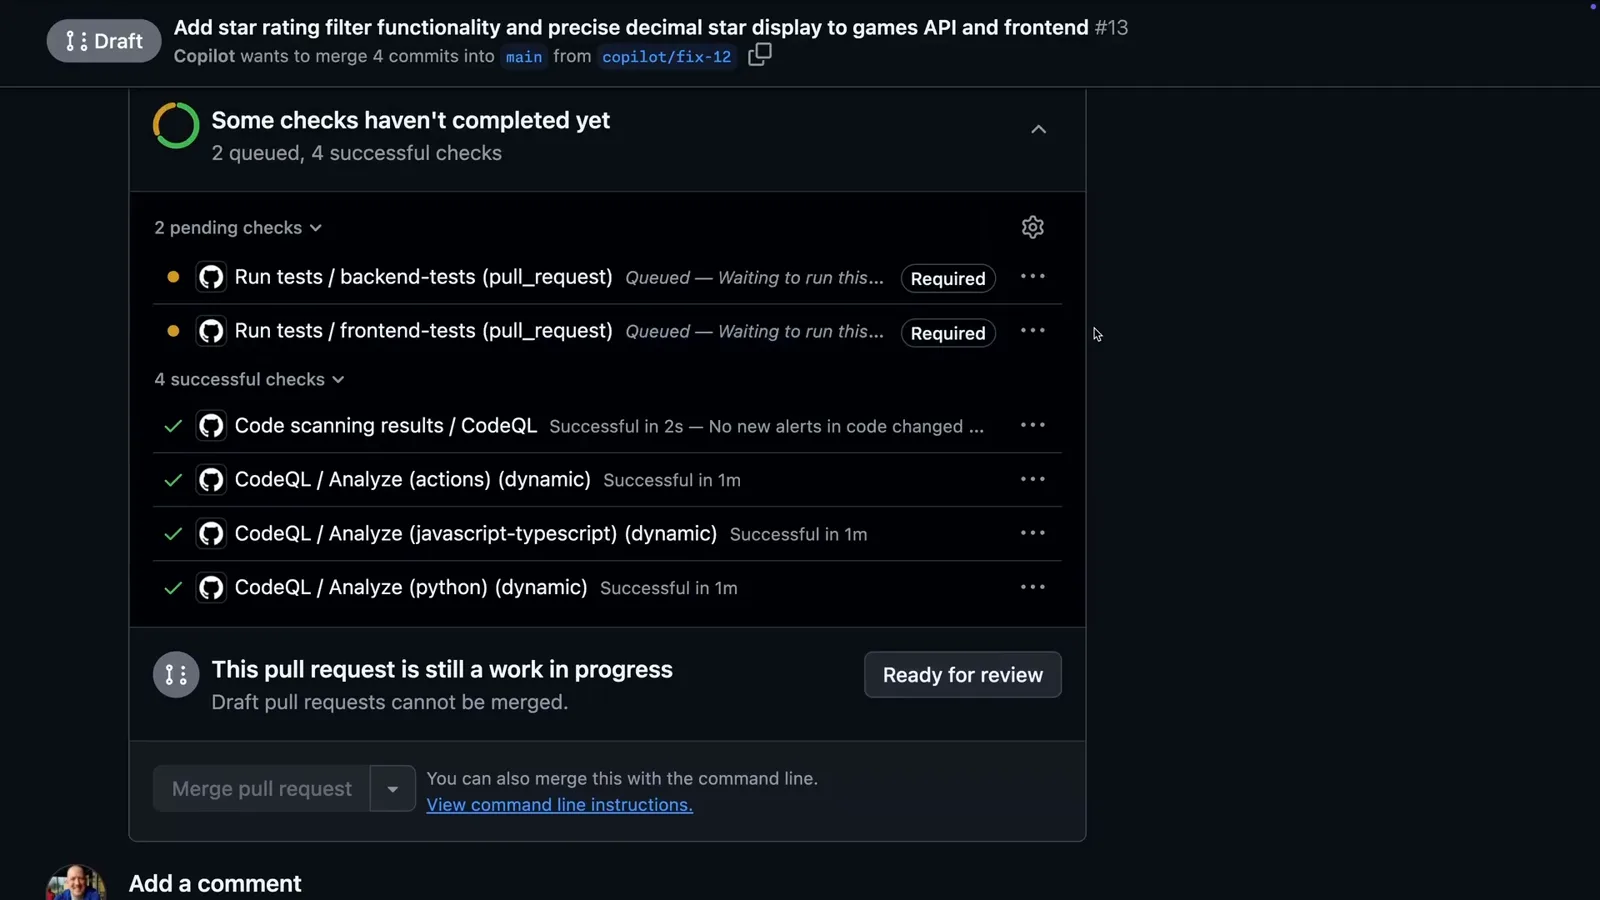
排队就是在等你:Copilot 的 PR 需要人类点一下,Actions 才会运行。去视频 4:18 处观看